What is End-to-End Encryption?
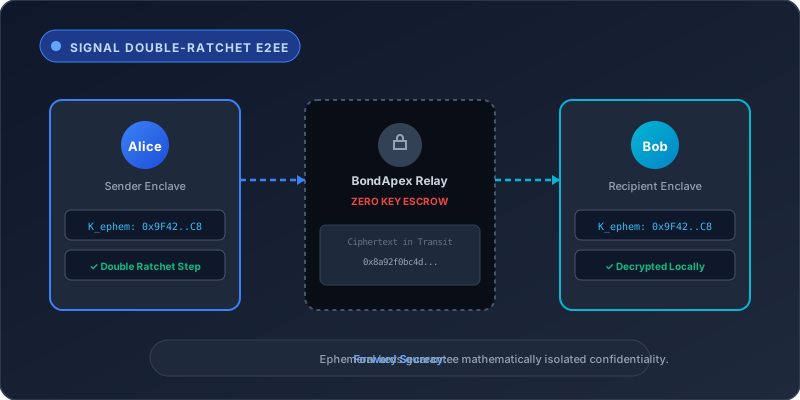
End-to-end encryption (E2EE) is a cryptographic architecture ensuring that data is encrypted on the sender’s device and decrypted only by the intended recipient’s device. In transit across relay nodes, routers, or platform infrastructure, data remains an unreadable ciphertext. Neither third parties, internet service providers, nor BondApex servers hold the decryption keys.
How BondApex Implements the Signal Protocol
BondApex implements the state-of-the-art Signal Protocol featuring the Double-Ratchet Algorithm and Extended Triple Diffie-Hellman (X3DH) key agreement. When initializing a chat session, ephemeral pre-keys are exchanged to establish a root secret. Every subsequent message triggers a cryptographic ratchet step, deriving fresh, forward-secret keys. If an individual message key were ever compromised, previous and future messages remain mathematically protected.
Zero-Knowledge Architecture: What Servers Can & Cannot See
Transparency is fundamental to our security model. Under our Zero-Knowledge architecture: BondApex servers CANNOT inspect message text, voice recordings, media attachments, or WebRTC call media. Private encryption keys reside strictly in your device’s hardware secure enclave or encrypted local storage. Server infrastructure handles only authenticated packet routing and encrypted message delivery queues.
Safety Numbers & Key Fingerprint Verification
To safeguard against potential man-in-the-middle attacks on public networks, BondApex provides verifiable Safety Numbers. Each 1-on-1 chat and circle generates a unique 60-digit cryptographic fingerprint and QR code. Users can scan or compare fingerprints out-of-band to confirm that their end-to-end connection is direct and unintercepted.
Secret Chats & Ephemeral Disappearing Messages
For sensitive communication requiring zero local residue, BondApex includes Secret Chats. These sessions utilize device-bound ephemeral keys that cannot be exported to secondary sessions, combined with configurable self-destruct timers ranging from 5 seconds to 24 hours and active screenshot detection alerts.
Continuous Security Audits & Cryptographic Integrity
Our cryptographic implementation is subject to regular third-party audits by independent security research firms. We maintain an active vulnerability disclosure program and open technical documentation, ensuring that our privacy guarantees are verifiable and grounded in robust mathematics.